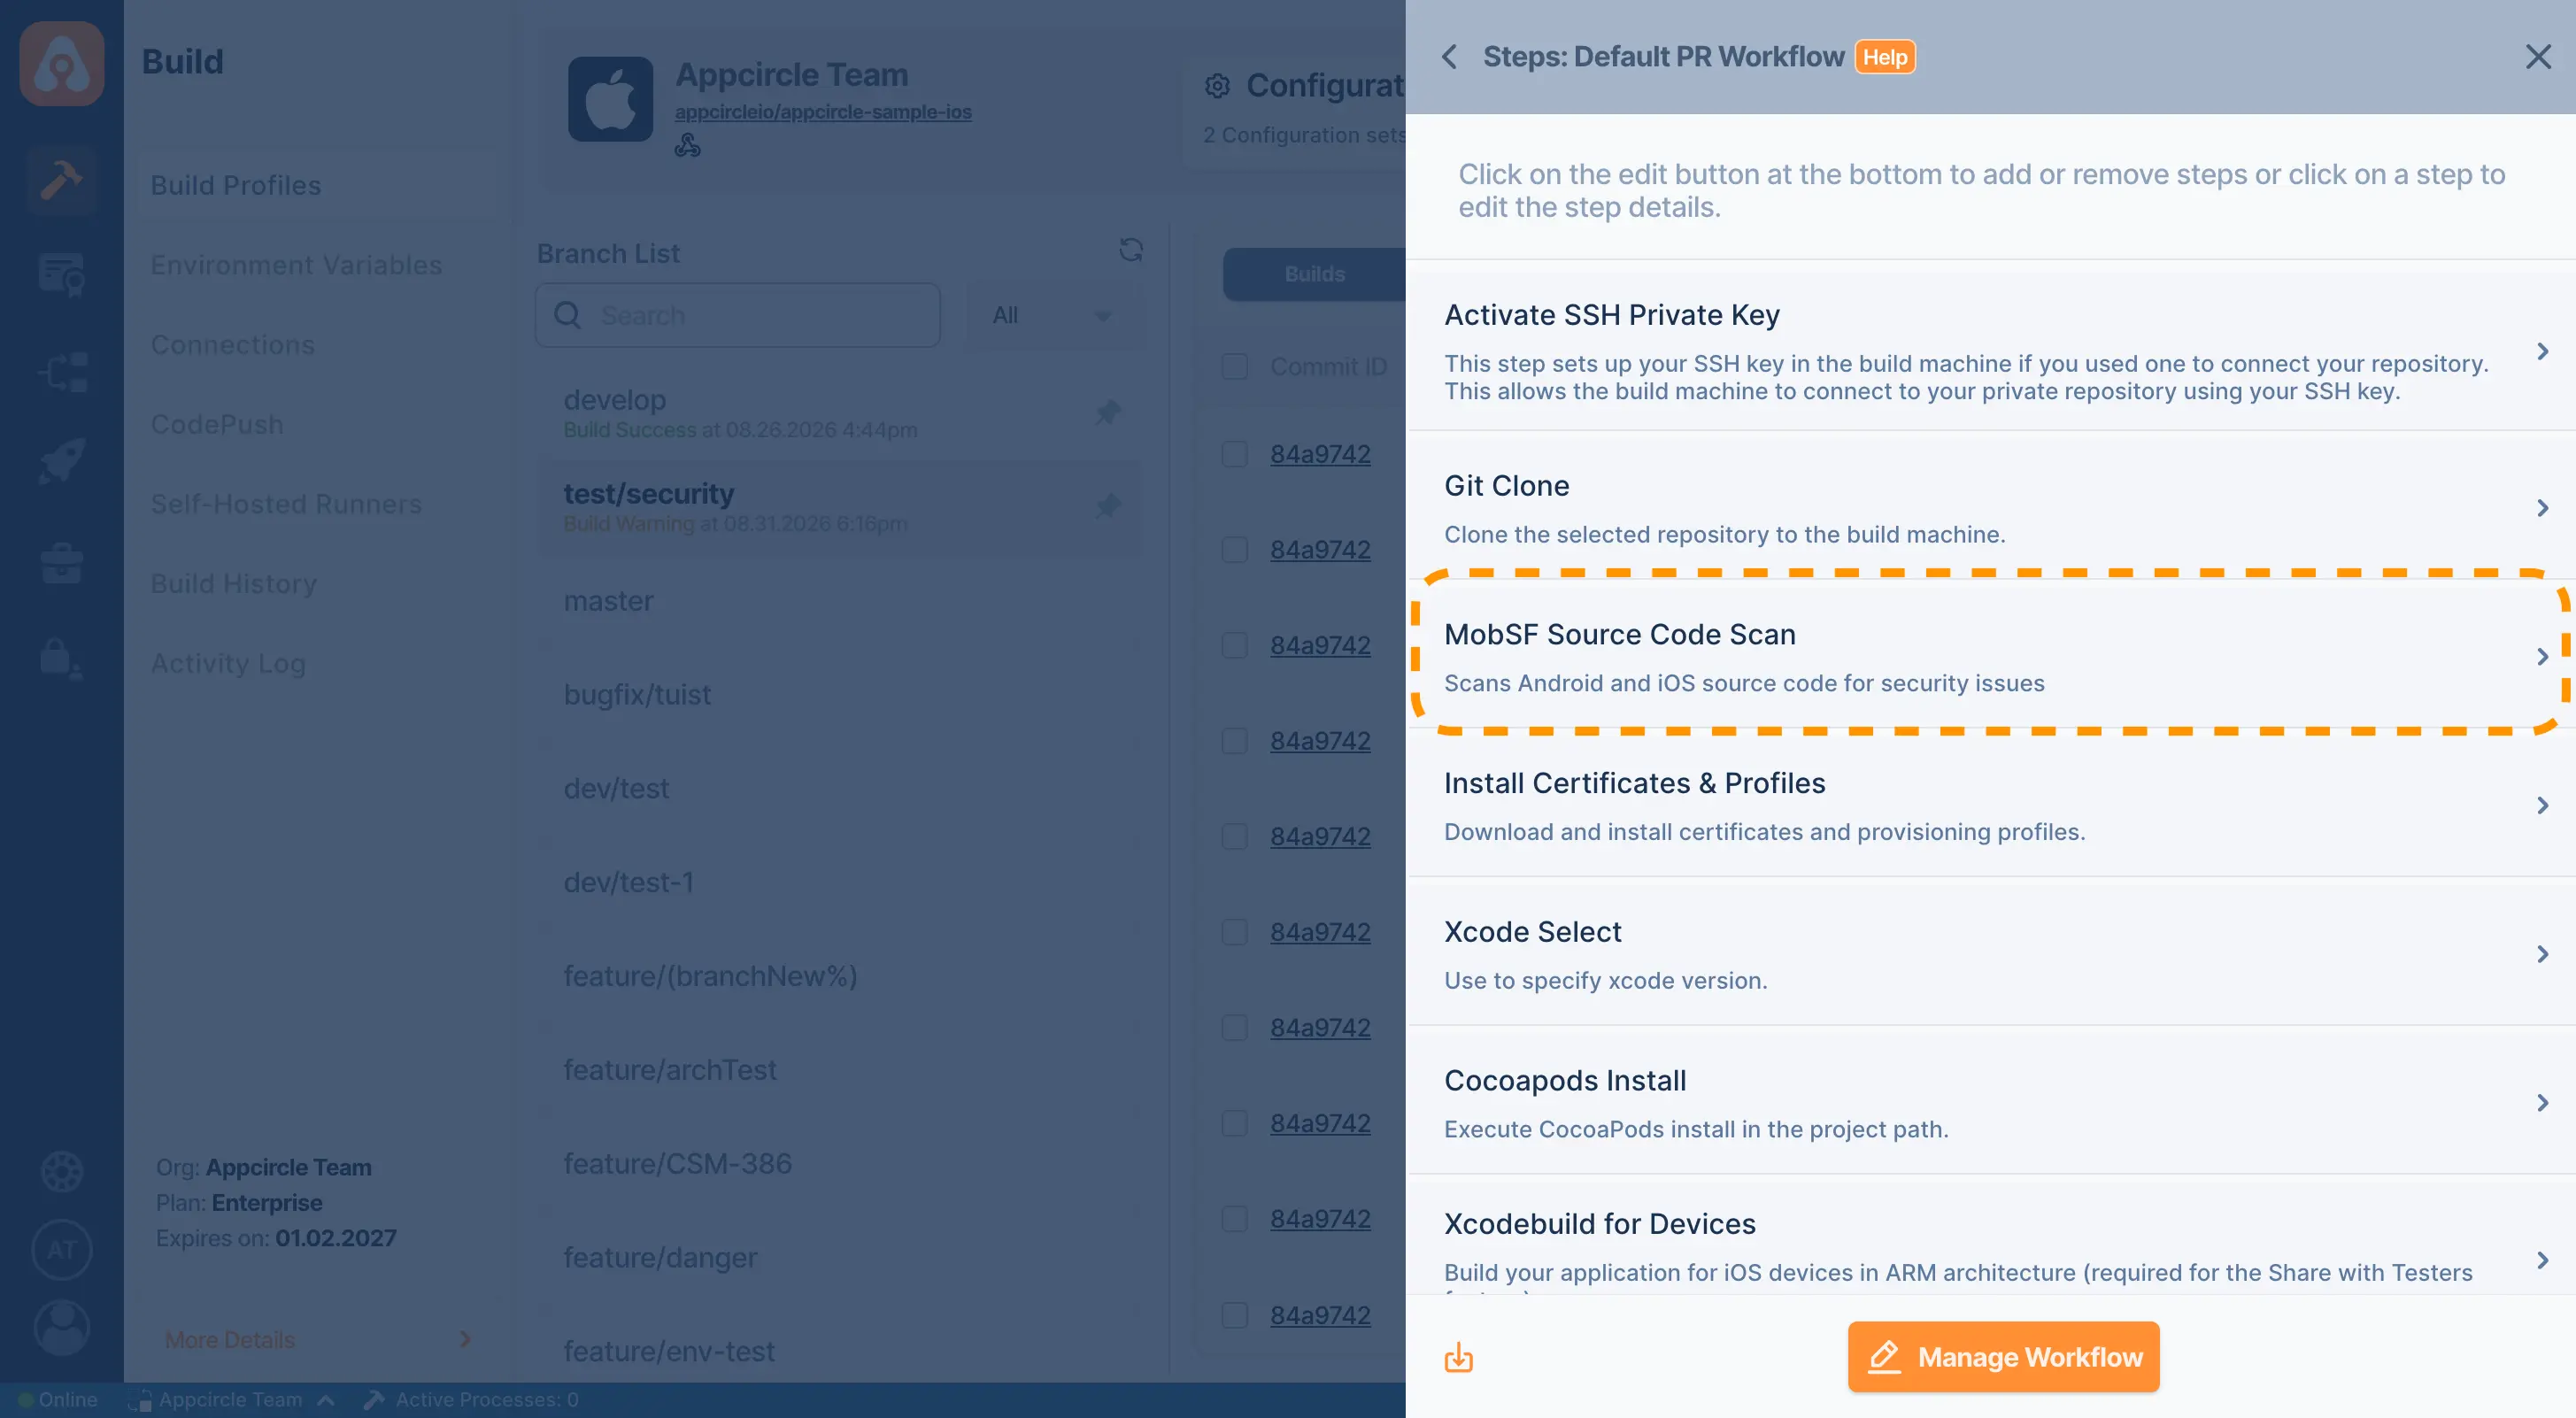
MobSF Source Code Scan
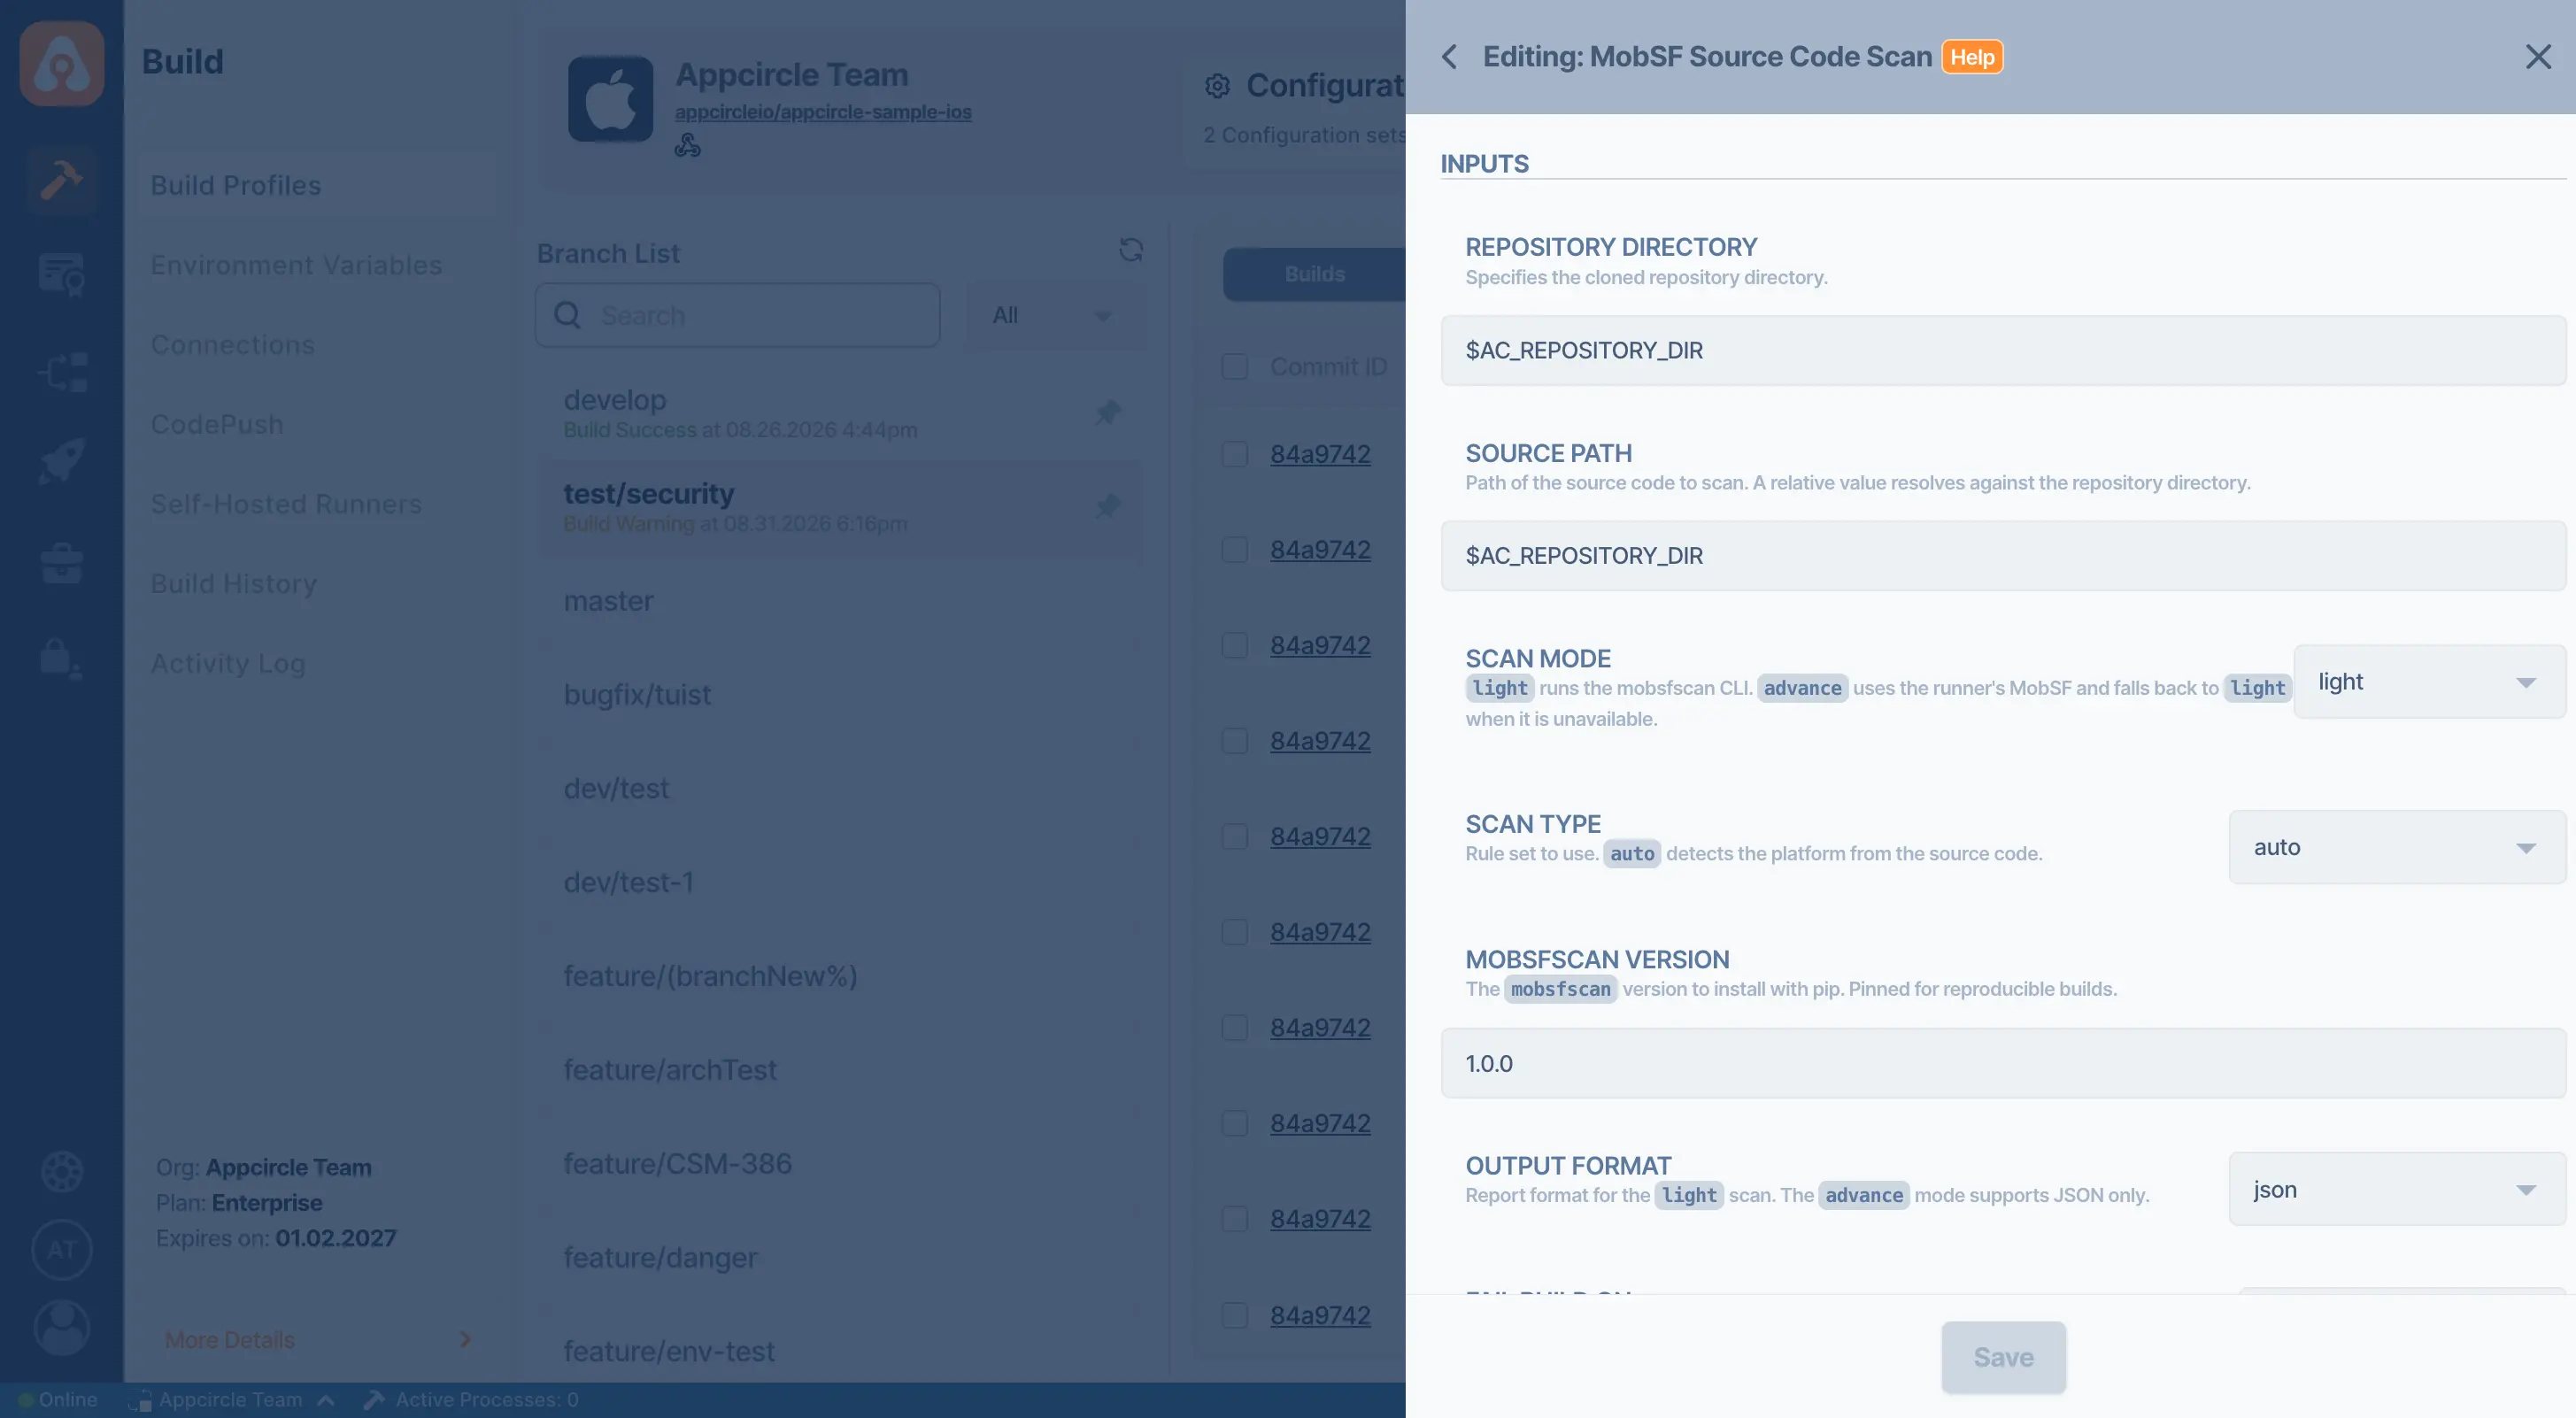
Integrating MobSF source code scanning in Appcircle's CI/CD pipelines provides automated static analysis of mobile application code, detecting insecure coding patterns and hardcoded secrets before they reach a release build.
Key Benefits
Mobile-Specific Static Analysis: Scans Java, Kotlin, Android XML, Swift, and Objective-C source for insecure mobile coding patterns using MobSF's own rule set, rather than relying on generic SAST rules that miss platform-specific risks.
Standards-Aligned Findings: Maps each finding to CWE and OWASP MASVS references, so results connect directly to the mobile security frameworks your audit and compliance processes already reference.
Configurable Build Gate: Applies a severity threshold that either fails the build or reports findings without blocking, letting you enforce a security baseline before code is merged or distributed.
Portable Report Formats: Produces SARIF, JSON, and SonarQube-compatible output alongside the scan, so findings can flow into your existing code scanning, AppSec, or vulnerability management tooling without custom conversion.
Points to Consider
Scan Scope Configuration: Define exclusions for generated code, vendored dependencies, and test fixtures so results stay focused on code your team actually owns and can act on.
Severity Model: The scanner reports findings at two levels rather than a granular scale, so calibrate your gate threshold and triage expectations around that model instead of assuming a five-tier severity system.
Failure Policy: Decide per workflow whether findings should block the build or report only. A common pattern is enforcement on release branches and advisory mode on feature branches.
Analyzer Version Management: Pin the scanner version for reproducible results across builds, and review upstream rule updates periodically so new detections are adopted deliberately rather than arriving unannounced.

For more information on setup and usage, please visit Appcircle Technical Documentation
FAQs
What is MobSF Source Code Scan?
Which languages and source types does it analyze?
Can MobSF findings block my build?
What report formats does the scan produce?
How are findings mapped to security standards?
How does this differ from MobSF Binary Scan?
Get Started with Appcircle
Save time, reduce costs, and increase developer productivity
Get informed about news, new releases, and mobile DevOps.